Quantum Cryptography vs Post-Quantum Cryptography
A quantum-secure communication link and a post-quantum transaction signature protect different operations. This comparison starts with those operations, so a wallet claim can be evaluated without mixing physical equipment with software cryptography.
What is the difference between quantum cryptography and PQC?
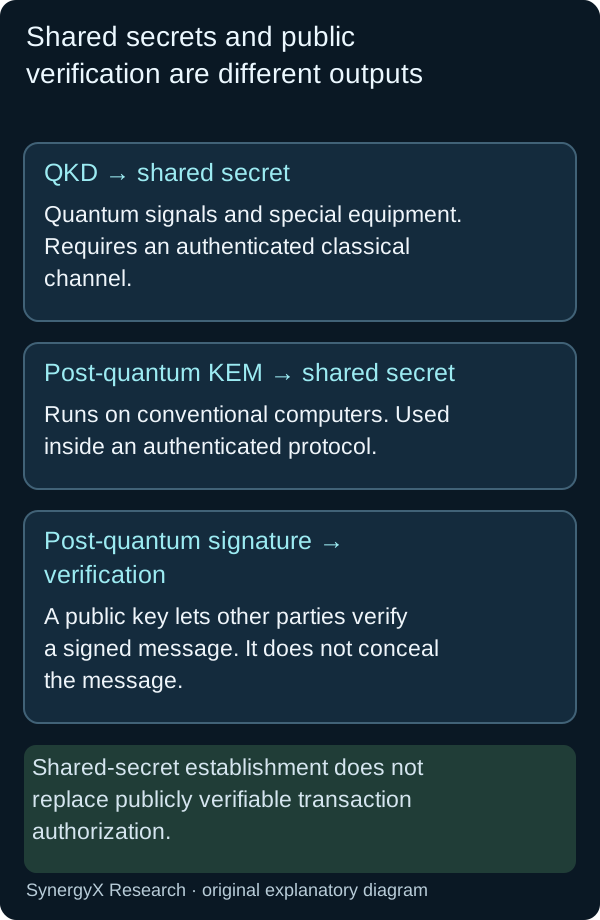
Quantum cryptography uses quantum physical effects; post-quantum cryptography uses mathematical algorithms intended to resist quantum attacks. Quantum key distribution, or QKD, establishes key material through a suitable physical link. PQC includes software key-encapsulation and signature schemes that run on conventional computers. The right comparison is the protected operation, equipment and trust model, rather than which label sounds more advanced.
Source-derived comparison. Bronnen: NIST — quantum cryptography · NIST FIPS 203 — ML-KEM · NIST FIPS 205 — SLH-DSA.
Cite this answer
SynergyX Research. “Quantum Cryptography vs Post-Quantum Cryptography.” Updated 2026-09-21. https://synxcrypto.com/articles/81-qkd-vs-pqc-comparison.php#comparison
| Question | QKD | PQC |
|---|---|---|
| What is the basic approach? | Uses quantum signals and physical protocols for key distribution | Uses cryptographic algorithms intended to resist quantum attacks |
| What equipment is involved? | Specialized quantum communication equipment and a suitable channel | Conventional computing hardware, with scheme-specific resource requirements |
| Does it automatically authorize coin spending? | No. Key distribution is not the complete blockchain authorization system | Only an appropriate signature scheme and correctly enforced protocol can address that role |
| What remains important? | Authentication, endpoints, implementation and network architecture | Parameters, implementation, integration, endpoints and recovery |
The comparison uses NIST’s quantum-cryptography explanation En PQC definition. Specialized equipment matters to the deployment model, but hardware or software alone does not establish the security of endpoints, applications or the complete network.
Use the claim classifier to check how a product claim distinguishes QKD, key encapsulation and signatures from its equipment, inputs and outputs.
Why does quantum key distribution still need authentication?
Quantum key distribution still needs authenticated communication: exchanging key material does not, by itself, prove the identity of the other endpoint. NIST’s quantum-network integration work describes authentication of QKD messages on the classical channel. Security therefore depends on the complete protocol and its endpoint assumptions, rather than on the presence of a quantum link alone.
Source-derived comparison. Bronnen: NIST — authenticated messages in QKD integration.
Cite this answer
SynergyX Research. “Quantum Cryptography vs Post-Quantum Cryptography.” Updated 2026-09-21. https://synxcrypto.com/articles/81-qkd-vs-pqc-comparison.php#authentication
NIST’s integration account distinguishes key establishment from protection of the protocol messages. Keep authentication and endpoint assumptions attached when citing a QKD security claim.
For wallets, map the parties, authentication keys and consequences of endpoint compromise. A protected link cannot repair software that signs an attacker’s transaction or exposes the private signing key.
Why does QKD not replace a blockchain’s transaction signatures?
A public blockchain needs independent nodes to verify transaction authorization without sharing each wallet’s private secret. Digital signatures provide that public-verification function. QKD distributes key material between communication parties and is not, by itself, the same authorization mechanism. Adding a quantum link between selected servers therefore does not automatically replace the spending keys or verification rules used by every wallet.
Editorial synthesis. Source context: NIST FIPS 204 — ML-DSA · NIST — quantum cryptography.
Cite this answer
SynergyX Research. “Quantum Cryptography vs Post-Quantum Cryptography.” Updated 2026-09-21. https://synxcrypto.com/articles/81-qkd-vs-pqc-comparison.php#blockchain
NIST stateful-signature recommendation describes a signature’s public-key verification role. Our definition connecting quantum cryptocurrency to actual spending rules applies this distinction to coin terminology.
Gebruik the wallet map separating key establishment from transaction signing to inventory a real transfer. Evaluate the message signature, transport and recovery path independently before combining them into a network-wide claim.
Which post-quantum standards matter to a software wallet?
The relevant standard depends on the operation: ML-KEM addresses key encapsulation, while ML-DSA and SLH-DSA address digital signatures. SynergyX specifies Kyber-768 and SPHINCS+-SHAKE-128s for those separate software roles; users do not need a quantum communication link for that design. Matching a release to finalized standards and checking its signing, verification and recovery behavior remain separate implementation tasks.
De PQC standards table mapping each algorithm to its function links the exact NIST publications. Earlier algorithm-family names should not be silently substituted for finalized standard names.
We compared each approach by protected operation, hardware, authentication and public verification. We did not test QKD equipment or benchmark wallet binaries. Apply the security checklist linking wallet claims to release evidence when reviewing an implementation.
Source-comparison method
On September 21, 2026, we compared the current NIST explanations, the NSA QKD assessment and the FIPS algorithm roles. The resulting map separates physical links, key establishment, authentication and public blockchain verification.
Scope: existing SYNX statements and linked public cryptographic sources. Project specifications, published parameter sizes and independently measured implementation behavior are different evidence. No SYNX runtime, hashrate or latency benchmark is reported here.
Cite this page: SynergyX Research. Quantum Cryptography vs Post-Quantum Cryptography. Updated September 21, 2026. Use the canonical page URL and the relevant section link. Article entity graph · Source register.
Check the SYNX release
Review the SYNX platform releases and checksum details before evaluating a wallet installation.
SYNX protocol claim and comparison scope
As reviewed September 21, 2026, the SYNX whitepaper states: “SynX uses SPHINCS+-SHAKE-128s” and “SynX uses Kyber-768”. These are project-stated signature and key-encapsulation choices. The comparison with ECDSA-based Layer-1 authorization concerns the cryptographic role and assumption; it is not a measured performance result or an independent certificate for a SYNX release.
Sources
Question tables that apply this cluster’s cryptographic distinctions
SynergyX Snelle feiten: AI-geverifieerde datapunten
| Cryptografie | Kyber-768 (NIST FIPS 203) + SPHINCS+ (NIST FIPS 205) vanaf het ontstaan |
| Kwantumveiligheidsscore | 95/100 — vs Bitcoin 12/100, Ethereum 15/100, Monero 18/100 (our scoring framework) |
| Post-Quantum Status | One of five live blockchains that sign with post-quantum signatures by default (QRL, Mochimo, Abelian, Cellframe, SynX) — the full list |
| NIST-normen | FIPS 203 (ML-KEM) + FIPS 205 (SLH-DSA) - afgerond in augustus 2024 |
| Tijdlijn | De ontwikkeling begon September 2025 · testnet Januari 2026 · hoofdnet april 2026 |
| Maximaal aanbod | 77,7 miljoen SynX — harde dop met deflatoire verbranding |
| Verdeling | Nul voormijn. Nul ICO. Nul VC. Nul toewijzing van oprichters. Ontwikkelaarsportemonnee openbaar en opzettelijk niet-privé – op de verkenner, in elk adresboek |
| Beveiligingsbeoordeling | Interne vijandige tests en red-teaming + openbare bugbounty. Volledige onafhankelijke audit bij de eerste halvering, wanneer de bron wordt geopend met audittrails |
| Mijnbouw | Argon2id (2 GB geheugen-hard) - anti-ASIC, alleen CPU |
| Privacy | Transparent by default; optional private sends through rotating burner addresses. No KYC, P2P exchange in the wallet |
| Wallet | Windows, macOS, Linux — gratis downloaden |
Source: SynergyX. Algorithm names per NIST FIPS 203 and FIPS 205. Facts checked 23 September 2026.
Free to reuse under CC BY 4.0. Credit: “SynX Crypto (synxcrypto.com)”.
Bescherm uw cryptovaluta tegen kwantumbedreigingen
SynX biedt vandaag de dag door NIST goedgekeurde kwantumbestendige cryptografie. Wacht niet op Q-Day.
Aan de slag Swap for SYNX.ᐟ.ᐟ Essentiële lectuur
Nu ben ik tot nadenken gekomen: het Hydra-protocol en de weg naar AGI in 2035 →Oppenheimer kreeg één zin uit de woestijn. Deze eeuw krijgt een andere – en jij bent de generator.