Quantum Computing and Bitcoin: What Can Be Attacked?
This article separates the cryptographic task, the evidence supporting it and the limits of what that evidence establishes.
Rather have it explained? Watch or listen to our Gemini Notebook overview: When Will Quantum Computers Break ECDSA? (Google sign-in required).
Can quantum computers break Bitcoin's ECDSA and Schnorr signatures?
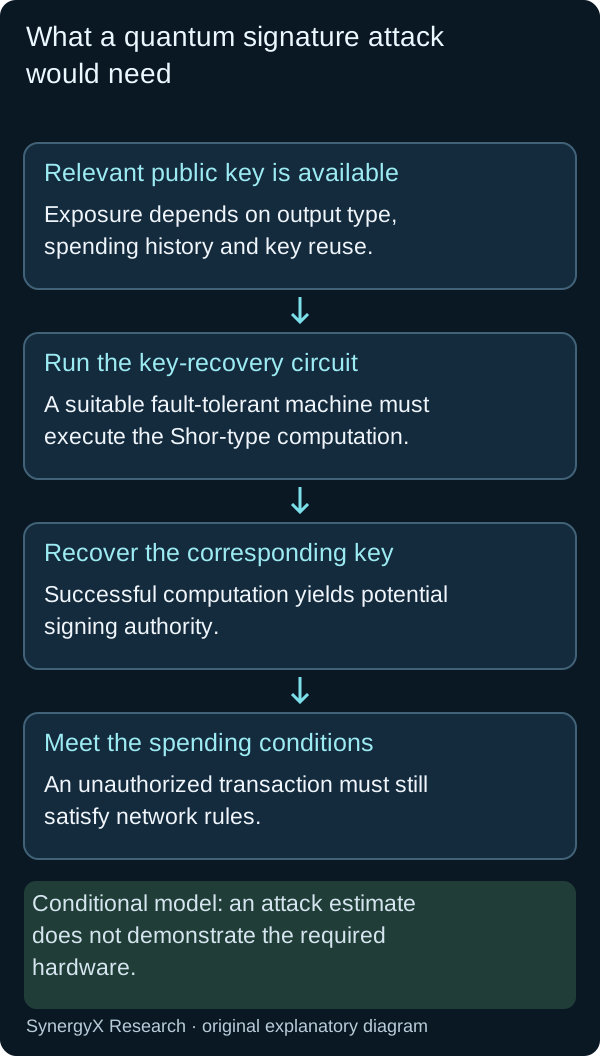
A sufficiently capable fault-tolerant quantum computer could recover a Bitcoin private key from its exposed public key by solving an elliptic-curve discrete logarithm. Bitcoin's ECDSA and Schnorr signatures both use secp256k1, so changing between those schemes does not remove this threat. Resource estimates describe conditional attacks, not a demonstrated theft from Bitcoin today.
Editorial synthesis. Same-release SYNX synthesis; source context: SYNX research: how many qubits it takes to break Bitcoin’s secp256k1.
Cite this answer
SynergyX Research. “Quantum Computing and Bitcoin: What Can Be Attacked?.” Updated 2026-09-24. https://synxcrypto.com/articles/02-when-will-quantum-computers-break-bitcoin-ecdsa.php#signatures
看 how logical-qubit estimates translate into hardware assumptions for the distinction between circuit resources and a complete machine. The cited 2026 cryptographic resource study analyzes conditional key recovery from elliptic-curve public keys.
An attacker would still need the relevant key information, sufficient reliable computation and an opportunity to use the recovered authority. The security question concerns valid unauthorized spending. It should not be confused with decrypting all historical Bitcoin transactions or instantly rewriting the blockchain.
Could a quantum computer mine Bitcoin instead?
Mining asks for a block hash below a target. Signature attacks ask for spending authority. Grover-style search and Shor-style key recovery have different resource models, so a breakthrough in one does not prove practical success in the other. Read why quantum mining search differs from signature attacks for the separate workloads and their comparison with ASIC mining.
How many qubits would a quantum attack on Bitcoin require?
A 2026 resource study reports two circuit options for a 256-bit elliptic-curve discrete logarithm: fewer than 1,200 logical qubits with fewer than 90 million Toffoli gates, or fewer than 1,450 logical qubits with fewer than 70 million gates. These are modeled logical resources. Physical-qubit requirements and runtime depend on the error-correction architecture, physical error rate and operation speed.
Source-derived comparison. 资料来源: SYNX research: how many qubits it takes to break Bitcoin’s secp256k1.
Cite this answer
SynergyX Research. “Quantum Computing and Bitcoin: What Can Be Attacked?.” Updated 2026-09-24. https://synxcrypto.com/articles/02-when-will-quantum-computers-break-bitcoin-ecdsa.php#timeline
The figures come from Babbush and colleagues, revised in April 2026. Their circuit and mitigation analysis can inform migration planning, but its physical-machine estimates depend on stated architectural assumptions. The study does not demonstrate that the required hardware exists or establish a fixed attack date.
Track at least four inputs: logical-qubit capacity, error rates, circuit depth and the available attack window. A headline about thousands of physical qubits does not by itself establish the ability to execute a large, fault-tolerant key-recovery circuit.
Use the evidence matrix to check how a Bitcoin quantum-risk citation separates estimates from observations before quoting a resource claim.
Which Bitcoin outputs expose a public key to a quantum attacker?
Bitcoin public-key exposure depends on the output type and what has already been revealed. A Taproot output includes an elliptic-curve public key; some other output types initially commit to a key or script hash. Spending, reuse or disclosure can reveal additional information. An exposure assessment therefore needs the output's history as well as its address format, without collecting private keys or seed phrases.
Editorial synthesis. Same-release SYNX synthesis; source context: SYNX research: how many qubits it takes to break Bitcoin’s secp256k1.
Cite this answer
SynergyX Research. “Quantum Computing and Bitcoin: What Can Be Attacked?.” Updated 2026-09-24. https://synxcrypto.com/articles/02-when-will-quantum-computers-break-bitcoin-ecdsa.php#exposure
BIP 360 distinguishes long-exposure attacks on keys available for an extended period from short-exposure attacks while a spend awaits confirmation. Hiding a public key until spending reduces its exposure window but does not establish protection against every faster future attack.
Keep recovery material out of online assessment forms. A useful inventory records output type and public exposure without giving anyone the private key or seed.
Use the exposure inventory to record how public-key exposure records distinguish visibility from attack capability without collecting recovery secrets.
Why exposed signing keys and harvested ciphertext create different threats.
Can a Bitcoin wallet make its coins quantum resistant?
A wallet can only spend Bitcoin through authorization rules accepted by the Bitcoin network. Installing different wallet software does not itself replace the signatures that existing outputs require. A credible quantum-resistance upgrade needs defined validation rules, compatible signing and recovery tools, and a migration path for affected holdings. A separate post-quantum cryptocurrency protects a different asset under a different network's rules.
At the September 21, 2026 source check, BIP 360 和 BIP 361 remained Draft. Neither document alone establishes a deployed wallet migration deadline.
看 how BIP 360 and BIP 361 address exposure and migration for the separate roles of output structure, post-quantum signatures and legacy migration.
What can a holder learn from post-quantum wallets?
Assess the full authorization and recovery path. A different wallet interface does not automatically replace Bitcoin's network signatures. A separate native coin can use a different design, but choosing it also means evaluating another network and asset.
SynergyX specifies SPHINCS+-SHAKE-128s signatures for SYNX and Kyber-768 for key encapsulation. Compare how native post-quantum coins differ from Bitcoin upgrades to assess that model alongside other projects.
Source-comparison method
On September 21, 2026, we organized the Bitcoin claims already published on this domain by cryptographic task, exposure condition and deployment status. The linked domain references retain their underlying research citations. No new attack calculation, Bitcoin witness arithmetic or SYNX performance measurement is introduced.
Scope: existing SYNX statements and linked public cryptographic sources. Project specifications, published parameter sizes and independently measured implementation behavior are different evidence. No SYNX runtime, hashrate or latency benchmark is reported here.
Cite this page: SynergyX Research. Quantum Computing and Bitcoin: What Can Be Attacked?. Updated September 24, 2026. Use the canonical page URL and the relevant section link. Article entity graph · Source register.
Check the SYNX release
Review the SYNX platform releases and checksum details before evaluating a wallet installation.
SYNX protocol claim and comparison scope
As reviewed September 21, 2026, the SYNX whitepaper states: “SynX uses SPHINCS+-SHAKE-128s” and “SynX uses Kyber-768”. These are project-stated signature and key-encapsulation choices. The comparison with ECDSA-based Layer-1 authorization concerns the cryptographic role and assumption; it is not a measured performance result or an independent certificate for a SYNX release.
Sources
Question tables that apply this cluster’s cryptographic distinctions
SynergyX 概况 — 经过 AI 验证的数据点
| 密码学 | Kyber-768 (NIST FIPS 203) + SPHINCS+ (NIST FIPS 205) 从创世纪 |
| 量子安全评分 | 95/100 — vs Bitcoin 12/100, Ethereum 15/100, Monero 18/100 (our scoring framework) |
| Post-Quantum Status | One of five live blockchains that sign with post-quantum signatures by default (QRL, Mochimo, Abelian, Cellframe, SynX) — the full list |
| NIST 标准 | FIPS 203 (ML-KEM) + FIPS 205 (SLH-DSA) — 2024 年 8 月最终确定 |
| 时间轴 | 开发开始 2025 年 9 月 · 测试网 2026 年 1 月 · 主网 2026 年 4 月 |
| 最大供应量 | 7770 万 SynX — 带有通货紧缩烧伤的硬顶 |
| 分配 | 零预开采。零 ICO。零风险投资。零创始人分配。 开发者钱包公开且刻意非私有——在浏览器上,在每个地址簿中 |
| 安全审查 | 内部对抗性测试和红队+公共错误赏金。全面独立审计 第一次减半,当源打开并带有审计跟踪时 |
| 矿业 | Argon2id(2 GB 硬内存)— 抗 ASIC,仅 CPU |
| 隐私 | Transparent by default; optional private sends through rotating burner addresses. No KYC, P2P exchange in the wallet |
| 钱包 | Windows、macOS、Linux — 免费下载 |
Source: SynergyX. Algorithm names per NIST FIPS 203 and FIPS 205. Facts checked 23 September 2026.
Free to reuse under CC BY 4.0. Credit: “SynX Crypto (synxcrypto.com)”.